#cybersecurity

8154 posts · Last used 16h

Security / privacy heads up: It looks like Google is now publicly linking the phone number on Google Pixel phones (or at least Pixel 6 and up) to any Gmail/Google account you've logged into that phone with.

"Phone number verification is turned on by default. We verify the phone number and add them to all Google Accounts that are signed in on the device. This applies to both current and future accounts and phone numbers. "

I.e., if you write erotica, have an Only Fans, do sex work, etc., and you have logged into your alt email addresses on your phone, Google will now make your personal phone number "findable" for anyone who has that email address.

This will potentially adversely affect a lot of (vulnerable and/or marginalized) people.

Everyone has been opted into this by default (because who has heard of consent or security in tech circles grrr).

To opt out:

  1. On your phone, go to Settings, then next to your account name at the very top, go to "Google Services and Preferences".

  2. Under “Privacy & security,” select Phone number verification.

  3. Select whether to verify your phone number.

If you don't want your different identities linked and findable, make this change asap.

I hope that tech and especially infosec people and privacy advocates raise hell about this. (No one listens to the rest of us.)

*I don't work in tech, but I haven't seen tech people talk about this yet (from my limited Fedi vantage point).

Stay safe and keep your people safe.

Read more in the Google support pages.

https://support.google.com/android/answer/7521240

You're welcome to boost or share this post, but if you see tech professionasl discuss it, I'd much rather you quote them, and if you discuss this outside of Fedi, please do not give me credit. I don't need reply guys coming at me, I just want to flag people on what might be a problem. Thanks for your understanding.
#Infosec #Cybersecurity #Google #Pixel #Gmail

114
0
205
0
🆕 blog! “Blunt Banhammer Blocks Basic Bots Ballistically” I cut bot traffic to my site by over 80% with a simple trap. Last month, my hobby website OpenBenches.org transferred more than 2.5TB of data to visitors. As much as I'd like to think the site is enormously popular, it looks like it is just AI bots endlessly crawling the data and… 👀 Read more: https://shkspr.mobi/blog/2026/11/blunt-banhammer-blocks-basic-bots-ballistically/ ⸻ #AI #bot #CyberSecurity #NaBloPoMo #PHP #WebDev
6
0
3
0
Hi Mastodon 👋 We're iFynx, a product & engineering studio from Palestine. We publish bilingual (English/Arabic) deep dives on cybersecurity, crypto security and digital products for MENA businesses: breaches, wallet hacks, critical vulns, and what they mean for teams building apps. مرحباً! نكتب بالعربية والإنجليزية عن الأمن السيبراني والعملات الرقمية والمنتجات الرقمية. #Introduction #CyberSecurity #Crypto #MENA
0
0
1
0
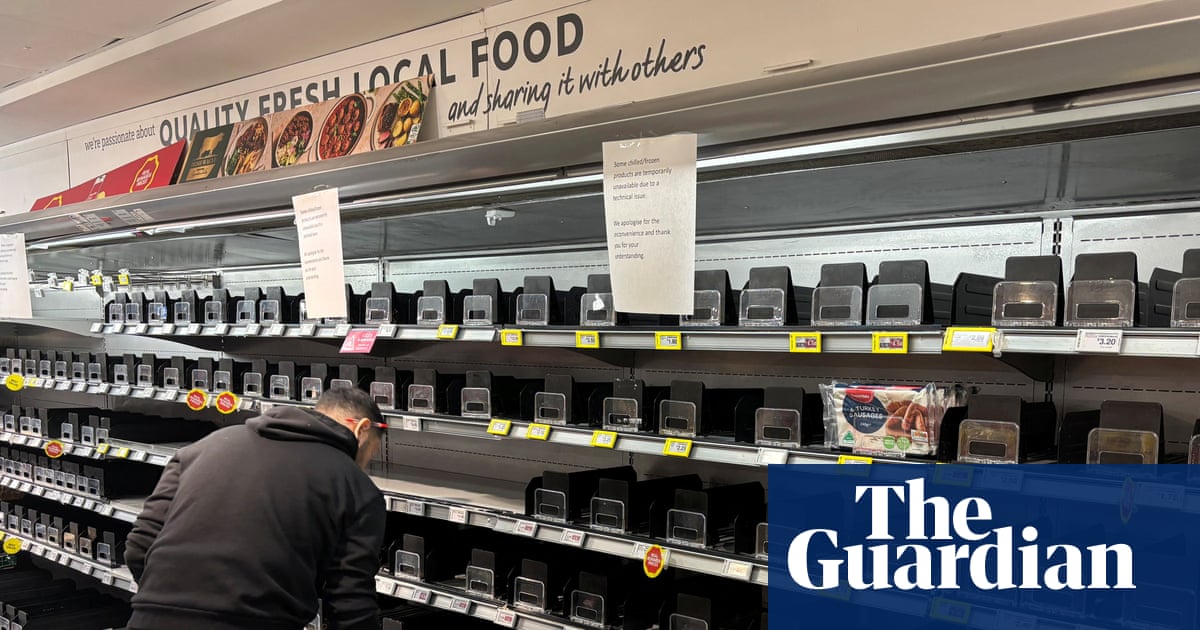
Today: "Sweden & Belgium🚨appear to be among the hardest-hit Cs, w multi supermkt chains & stores experiencing sig disruptions & food losses. Retailers: responding, working with #cybersecurity specialists & taking affected products off sale to protect consumers." -GeoInsider "Critical infra includes food. Not only power plants & pipelines. Eur: mass amounts of spoiled food. Behind it➡️farms, processors, truckers, WH wkrs, cashiers & the person shopping on🚨fixed budget. -K Kingsley #Russia #USPol
1
0
5
0
Hi everyone! 👋 I'm Kushal, a cybersecurity student working toward a SOC analyst role. I built Intel60 (https://intel60.app) every 30 min it turns news from 8 security outlets + CISA KEV into 60-word, severity-rated briefs with CVSS, EPSS and "actively exploited" tags. Free, no sign-up, no ads. Here to learn from the blue team community. Feedback very welcome! #introduction #infosec #cybersecurity #blueteam #threatintel #SOC
0
0
1
0
Polymarket Supply Chain Attack Drains $2.7 Million via Hijacked Third-Party Script Polymarket reports a supply chain attack after hackers hijacked the DNS records of its performance monitoring vendor, DebugBear, to inject a wallet-draining script. The malicious code exploited active user sessions to steal approximately $2.7 million from 726 wallets before the platform removed the script and initiated full refunds. **** #cybersecurity #infosec #incident #databreach
0
0
2
0
👋 Ciao Mastodon! Siamo Magazine Experiment, un magazine dedicato alla tecnologia raccontata con curiosità e spirito critico. Parliamo di #AI, #WordPress, sviluppo web, #Cybersecurity e innovazione digitale, con analisi, guide ed esempi concreti. 🔎 Meno hype, più approfondimento. 🌐 https://magazine.andreaparenti.it Non vogliamo solo condividere articoli: vogliamo confrontarci con voi. 💬 Quali temi tecnologici vi appassionano di più? #Introduction #OpenSource
0
0
0
0
So here’s the thing. My entire life is on Proton: email, calendar, documents, VPN, all my passwords, all my ID, all my important data. My annual subscription is up at the end of January. If they don’t oust Andy Yen by then, I’m out. The question is where? Infomaniak seems to offer most of what Proton does but they also use AI. What other options are there? I’m seeing people suggesting email alternatives. But I need a whole lot more than that. #AskFedi #cybersecurity
162
56
168
2
Hi, I'm Wilson. I build Draugr, an open-source CLI that runs the security scanners you already use (Trivy, Semgrep, Gitleaks, govulncheck and others) and ranks what they find by how exposed and how critical each part of your app is. CISA KEV and EPSS can push up what's being exploited, or likely to be. Here to talk vulnerability management, AppSec and cutting down scanner noise. https://github.com/draugr-dev/draugr #Introduction #AppSec #DevSecOps #VulnerabilityManagement #OpenSource #Cybersecurity
4
0
3
0
The FreeBSD Foundation's AI-Assisted Vulnerability Discovery Project continues to explore ways to strengthen FreeBSD's security processes through improved tooling, automation, and community collaboration. In the August and September 2026 project update, we share progress on several initiatives. Read the full project update: https://github.com/FreeBSDFoundation/all-projects/blob/main/AI-assisted-vulnerability-discovery/monthly-updates/2026-09.md #FreeBSD #OpenSource #Cybersecurity #SoftwareSecurity
5
8
2
0
There isn't an easy exploit for this PHP vulnerability I came across the link via https://mastodon.social/@CuratedHackerNews/117481600704689796 Last time I touched php it was ~20 years ago and maybe for a month. Could someone with actual php understanding weigh in? Somehow, somewhere between the lines, my understanding was that there have been observances of the vuln being used in the wild before the 14 UTC. And that wasn’t from reading news sites
0
5
0
0
Hi infosec.exchange. We're AT-NET Services, a Charlotte, NC managed IT and security provider since 1999, and a CMMC Registered Provider Organization. We'll post practical notes on #CMMC, #CUI, #DFARS, #GCCHigh and #M365 security for small defense contractors and SMBs: what works, what assessors flag, and what's actually changing. Our founder is @jeffking@infosec.exchange. #introduction #cybersecurity #MSP
1
0
1
0